Quick Summary
A technical and regulatory guide for UAE compliance officers and IT procurement leads evaluating digital KYC and onboarding software against CBUAE and Ministry of Economy requirements.
Financial institutions, Corporate Service Providers (CSPs), and Designated Non-Financial Businesses and Professions (DNFBPs) across the United Arab Emirates are rapidly shifting from paper-heavy, manual onboarding workflows toward automated eKYC solutions. However, procuring digital onboarding technology introduces complex regulatory obligations. Regulators in the region, including the Central Bank of the UAE (CBUAE) and the Ministry of Economy (MoE), require that digital client onboarding maintains the same rigor—and in many cases, superior data integrity and fraud prevention—as face-to-face verification.
When selecting software solutions (such as Cygnus Identia or similar enterprise compliance suites), risk managers, compliance officers, and IT leaders must ensure the technology strictly adheres to federal Anti-Money Laundering and Counter-Terrorism Financing (AML/CFT) frameworks. A failure in vendor validation or technological capability can lead to regulatory reprimands, administrative fines, and severe legal exposure. This guide provides an actionable framework for evaluating digital KYC vendors against current CBUAE standards and Ministry of Economy regulations.
The Evolution of Digital Client Onboarding in the UAE
Digital transformation initiatives in the UAE financial and professional service sectors have accelerated under national digital identity frameworks. The integration of UAE PASS and biometrics has established a benchmark for digital identity verification. However, implementing an eKYC platform requires more than dynamic facial recognition or optical character recognition (OCR) scanning; it demands end-to-end integration with enterprise AML risk scoring, automated Customer Due Diligence (CDD), Enhanced Due Diligence (EDD), and real-time sanctions screening.
For banks, exchange houses, finance companies, real estate brokerages, auditors, and trust service providers, regulatory compliance cannot be outsourced to a software vendor. While a third-party vendor provides the technological infrastructure, the regulated entity remains fully liable under UAE AML laws for any compliance deficiencies, identification errors, or missed sanctions matches.
Key Regulatory Frameworks Governing eKYC in the UAE
To establish a compliant digital onboarding process, compliance teams must understand the specific rules established by federal regulators and sectoral supervisors:
1. CBUAE Standards for Licensed Financial Institutions (LFIs)
The CBUAE issued explicit guidance regarding digital customer onboarding and eKYC systems. LFIs are required to implement robust risk-based policies for non-face-to-face customer relationships. Key compliance prerequisites include:
- Reliable Digital Identity Verification: Utilization of official, tamper-evident digital identity systems such as UAE PASS or cryptographically verified identity documents.
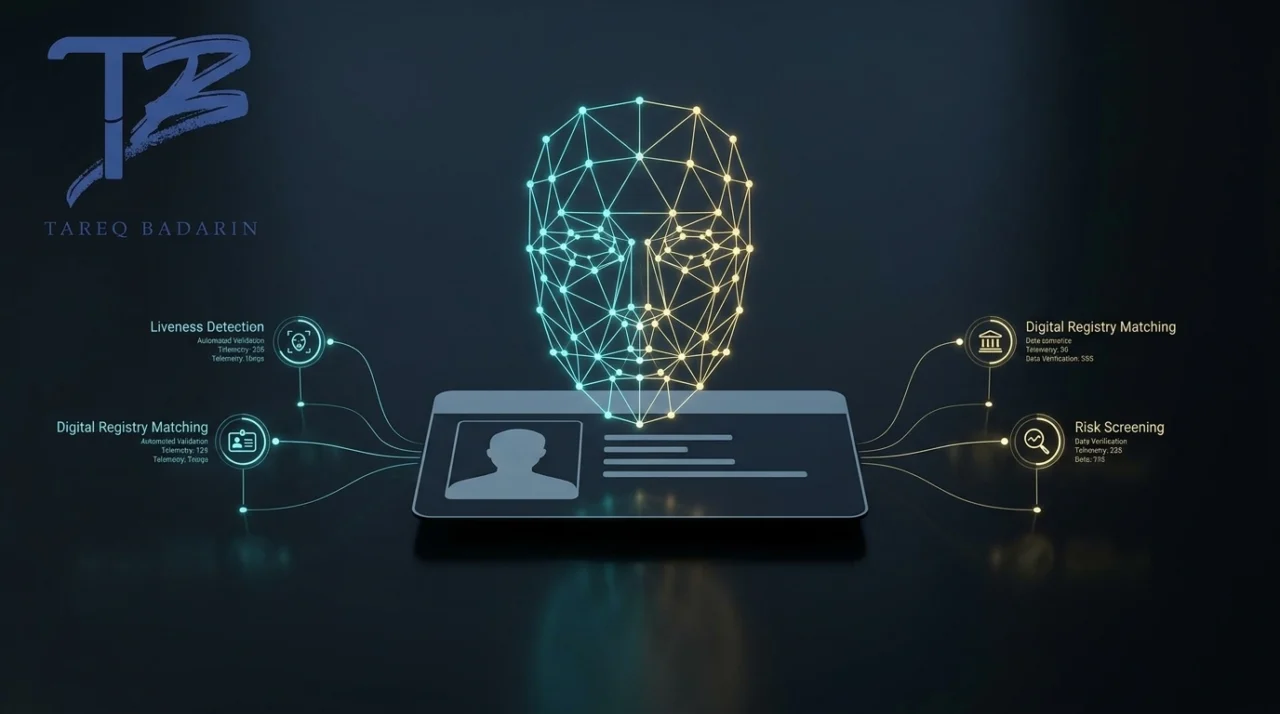
- Liveness Detection & Anti-Spoofing: Integration of passive and active liveness checks to prevent presentation attacks, deepfakes, and synthetic identity fraud.
- Data Recency & Integrity: Direct integration or verification against authoritative databases to confirm the current validity of Emirates IDs, passports, and commercial licenses.
- Automated Risk Assessment: Instantaneous risk scoring based on customer attributes, geographic footprint, transaction types, and political exposure (PEP status).
2. Ministry of Economy Regulations for DNFBPs
The Ministry of Economy oversees DNFBPs, including real estate developers and brokers, dealers in precious metals and stones, independent accountants, and corporate service providers. Under Federal Law No. 20 of 2018 and its amending decree law Federal Decree-Law No. 10 of 2025, DNFBPs must enforce thorough CDD measures prior to establishing a business relationship. For digital onboarding, the Ministry requires:
- Clear identification and verification of legal arrangements and Ultimate Beneficial Owners (UBOs) owning or controlling 25% or more of corporate entities.
- Verifiable audit trails documenting every step of the digital onboarding journey for inspection during supervisory examinations.
- Real-time screening against the UAE Local Terrorist List and the UN Consolidated List prior to account or transaction approval.
Core Evaluation Pillars for Digital KYC Software Validation
When evaluating digital KYC vendors in the UAE, compliance officers should assess platforms across six key operational and regulatory pillars:
Pillar 1: Biometric Verification & Liveness Detection
Static document collection (such as requesting a PDF scan of a passport) is no longer compliant or secure for non-face-to-face onboarding. Platforms must feature automated document verification paired with biometric validation. Ensure the platform adheres to international standards (such as ISO/IEC 30107 for presentation attack detection) to prevent sophisticated spoofing using photos, videos, or 3D masks.
Pillar 2: Integration with UAE PASS & Official Government Registries
A CBUAE-compliant digital identity onboarding system should support national digital identity infrastructure. UAE PASS integration allows instant, verified authentication for UAE residents. For corporate entities, the system should ideally interface with national commercial registers, economic development departments, or centralized registry systems to pull up-to-date corporate structures and commercial licenses.
Pillar 3: UBO Discovery & Corporate Structure Mapping
Verifying corporate entities digitally presents distinct challenges compared to individual customer onboarding. Software solutions must ingest corporate ownership charts, parse legal documentation across multi-layered holding structures, and identify the natural persons who ultimately control the business. The platform should automatically flag complex ownership structures, high-risk jurisdictions, or nominee arrangements requiring manual EDD intervention.
Pillar 4: Real-Time Sanctions, PEP, & Media Screening
Digital onboarding platforms must incorporate continuous, automated screening against relevant watchlists. Before an account is activated or a real estate transaction is finalized, the system must cross-check customer profiles against updated national and global sanctions lists. Key features to evaluate include:
- Native support for the UAE Executive Office for Control and Non-Proliferation (EOCN) targeted financial sanctions lists.
- Customizable fuzzy matching thresholds to catch variations in transliterated Arabic and foreign names while minimizing false positives.
- Instant alert routing to designated AML Compliance Officers (AMLCOs) for manual review before customer onboarding is finalized.
Pillar 5: System Auditability and Data Residency
In accordance with UAE data protection legislation and sector-specific cloud security guidelines issued by the CBUAE, candidate platforms must adhere to strict data localization and security measures. Compliance teams must confirm that client data, biometric templates, and identity documents are stored securely within UAE-based data centers (or compliant hybrid infrastructures) and encrypted both in transit and at rest. Every action taken by the software or human analyst must generate an immutable, time-stamped audit trail suitable for regulatory submission or independent AML audits.
Pillar 6: Configurable Risk-Scoring Engine
Off-the-shelf, rigid risk engines often lead to non-compliance. Your eKYC software must allow full customization of your firm’s Enterprise-Wide Risk Assessment (EWRA) parameters. Risk rules should be dynamically adjusted based on geography, client type, delivery channel, product complexity, and transaction values.
Comparing Traditional vs. CBUAE-Compliant Digital Onboarding
| Compliance Component | Traditional / Manual Onboarding | Compliant Digital eKYC Platform |
|---|---|---|
| Identity Verification | Manual review of physical IDs or unverified scanned copies | Biometric liveness detection & UAE PASS authentication |
| Sanctions & PEP Screening | Manual batch searching or delayed periodic checks | Automated, real-time pre-onboarding API screening |
| UBO Unwrapping | Paper-based organograms and physical legal document reviews | Automated parsing of corporate registries with visual mapping |
| Audit Trail | Dispersed physical files, emails, and shared network folders | Centralized, immutable digital logs with time-stamped actions |
| Processing Speed | 3 to 10 business days | Near real-time or minutes for low-risk profiles |
| Data Sovereignty | Variable paper storage and localized physical filing | Encrypted UAE-hosted cloud or secure hybrid infrastructure |
Technical & Regulatory Vendor Due Diligence Checklist
Before executing a software contract or integrating an eKYC API into your core banking or CRM enterprise systems, perform this regulatory checklist:
- Regulatory Alignment Review: Does the vendor’s roadmap explicitly address updates from CBUAE, Ministry of Economy, and FATF mutual evaluations?
- Security & Penetration Testing: Has the platform undergone recent third-party vulnerability assessments and penetration testing by certified cybersecurity firms?
- Model Validation: Has the automated risk-scoring logic and fuzzy-matching algorithm been validated to prevent systematic under-categorization of high-risk clients?
- goAML Integration Readiness: Can the platform export structured data and XML-compliant formats directly compatible with the UAE goAML portal for reporting Suspicious Transaction Reports (STRs) or Suspicious Activity Reports (SARs)?
- Fallback & Manual Escalation Workflows: Is there an efficient mechanism for compliance analysts to perform manual EDD when automated checks return inconclusive biometric matches or potential sanctions hits?
How Tareq Badarin Supports Digital Compliance Implementation
Adopting an eKYC platform is an operational transformation that requires careful regulatory alignment. Technology alone does not guarantee compliance; the technology must reflect tailored policies, procedures, and risk appetite parameters approved by senior management.
As a CAMS and ICA certified AML compliance expert operating in Dubai, UAE, in partnership with Farahat & Co., Tareq Badarin provides specialized advisory services to bridge the gap between technology selection and regulatory expectations:
- Digital Onboarding Framework Reviews: Validating that your digital client acquisition process meets all CBUAE guidelines and Ministry of Economy rules.
- Vendor & Software Compliance Validation: Conducting independent compliance audits of candidate eKYC platforms, risk models, and screening configurations.
- Custom Risk-Scoring Alignment: Translating your firm’s Enterprise-Wide Risk Assessment (EWRA) into digital risk-engine rules.
- Compliance Program Development: Updating internal AML policies, CDD/EDD SOPs, and governance documentation to reflect non-face-to-face onboarding realities.
- Staff & Officer Training: Delivering practical compliance training programs to ensure compliance teams effectively handle escalations, PEP alerts, and suspicious activity red flags.
Ensure your digital transformation strategy aligns with UAE legal standards before go-live. Consult with experienced compliance advisors to validate your digital KYC platform architecture today.
Operational Testing Framework for Validating Digital KYC Software and Algorithms
Selecting an eKYC vendor is only the initial step toward regulatory compliance. Before going live, compliance officers and risk management teams must rigorously test and validate the technical mechanisms of any digital customer onboarding system. Regulators like the CBUAE expect institutions to prove that their digital KYC platform compliance CBUAE standards are supported by empirical validation rather than vendor assertions alone. Establishing an internal operational testing framework ensures that algorithms perform accurately under real-world conditions without introducing systemic compliance vulnerabilities.
Phase 1: Biometric and Document Verification Accuracy Testing
To validate biometric performance and document authentications, institutions must test the software against diverse edge cases. Relying solely on happy-path demonstrations can lead to high false-acceptance rates during live operations.
- Presentation Attack Detection (PAD) Stress Testing: Test active and passive liveness engines using high-resolution printed photos, digital video playbacks on mobile screens, 3D silicone masks, and generative AI deepfake streams to ensure presentation attack detection holds up under variable lighting and angles.
- Substandard Document Ingestion: Subject the document verification engine to damaged physical Emirates IDs, worn passports, poorly illuminated mobile captures, and glare-heavy scans to measure optical character recognition (OCR) fallback accuracy.
- Digital Identity Cross-Matching: Verify that the platform correctly flags mismatch discrepancies when biometric liveness payloads are cross-referenced against stored data from UAE PASS or cryptographically signed chip data on physical Emirates IDs.
Phase 2: Sanctions and PEP Screening Precision Tuning
A critical requirement of eKYC solution compliance UAE banks and DNFBPs must enforce is the precise tuning of fuzzy matching algorithms. Overly broad matching rules cause operational gridlock through excessive false positives, while overly strict thresholds risk missing sanctioned individuals due to name transliteration differences.
| Test Scenario | Input Variation Example | Target Engine Behavior | Acceptance Standard |
|---|---|---|---|
| Arabic Name Transliteration | “Abdul Rahman” vs. “Abdelrahman” | Recognize phonetic equivalence across Latin script variations. | Match score exceeds internal risk threshold; routes to analyst. |
| Name Inversion & Order Shifts | “First Middle Last” vs. “Last First Middle” | Parse constituent name parts independently of positional order. | Correctly links profile to UAE EOCN / UN watchlist entry. |
| Noise Injection & Character Omission | Calculated typos or missing hyphens in corporate names | Apply configurable Levenshtein distance or Jaro-Winkler logic. | Flags potential match for manual EDD review without automatic rejection. |
Phase 3: UBO Unwrapping and Corporate CDD Logic Validation
Corporate onboarding requires software capable of handling intricate ownership structures. Evaluating digital KYC vendors UAE market participants consider must include validating automated UBO discovery logic against complex, multi-jurisdictional legal entities.
Testing teams should feed simulated complex corporate charts into the system—including entities with foreign parent companies, free zone entities, and layered holding structures across multiple offshore jurisdictions. The software must successfully parse legal documents, aggregate ownership percentages across indirect branches, and accurately identify natural persons holding 25% or more beneficial ownership or ultimate controlling interest, as mandated by Ministry of Economy digital client onboarding regulations.
Phase 4: Audit Trail Integrity and goAML Data Schema Verification
The final operational validation phase focuses on data integrity, auditability, and regulatory reporting capabilities. A platform must securely document every decision point and seamlessly connect with national reporting channels.
Compliance analysts must verify that the platform generates immutable, time-stamped logs for every automated approval, risk-score recalculation, and manual compliance override. Furthermore, technical teams must validate that customer profiles flagged for suspicious activity can instantly export structured, XML-compliant datasets directly aligned with the UAE goAML portal schemas. Conducting pre-launch dry runs of STR and SAR export workflows ensures that statutory reporting deadlines set by the Financial Intelligence Unit (FIU) can be met without technical friction.
Operationalizing Non-Face-to-Face Onboarding Governance
Deploying a compliant technology platform is insufficient on its own; financial institutions and Designated Non-Financial Businesses and Professions (DNFBPs) must update their operational governance frameworks to reflect non-face-to-face onboarding realities. Regulators enforce strict requirements regarding how remote customer acquisition is governed, documented, and overseen by senior management. Achieving digital KYC platform compliance CBUAE standards requires bridging the gap between automated software mechanisms and internal compliance controls.
Establishing Non-Face-to-Face CDD Policy Addendums
Standard Customer Due Diligence (CDD) and Enhanced Due Diligence (EDD) policies designed for in-person identification are inadequate for remote environments. Compliance teams must author formal addendums to their AML/CFT policy manuals that explicitly define the parameters of digital client acquisition under Ministry of Economy digital client onboarding regulations and CBUAE directives.
- Approved Digital Identity Schemes: Formal adoption of UAE PASS and cryptographically validated Emirates ID chip data as trusted primary identification methods.
- Risk Appetite and Ineligibility Rules: Clear definition of high-risk customer profiles, complex corporate structures, or foreign jurisdictions that are excluded from fully automated digital onboarding and require mandatory human intervention.
- Fall-Back Procedures: Standard operating procedures (SOPs) detailing step-by-step protocols when biometric liveness verification fails, document scanning OCR yields low confidence scores, or connectivity drops occur during remote sessions.
- Liveness Verification Standards: Policy mandates defining acceptable Presentation Attack Detection (PAD) standards and liveness confidence thresholds before an application can proceed automatically.
Senior Management Governance and Risk Engine Sign-Off
Under UAE regulatory standards, senior management retains ultimate responsibility for AML/CFT compliance, regardless of the automation level provided by eKYC solution compliance UAE banks adopt. Automated systems cannot execute self-directed changes to risk models or onboarding thresholds without explicit governance oversight.
Institutions must establish a formal change-management workflow for their digital risk engines. Any adjustment to fuzzy-matching thresholds, sanctions list updating frequency, country risk weights, or PEP scoring parameters must be documented, justified by enterprise-wide risk assessments, and formally signed off by the Designated Compliance Officer and Risk Committee. Minutes of these governance meetings must be archived alongside system revision logs to demonstrate effective oversight during CBUAE or Ministry of Economy regulatory examinations.
Manual Escalation and EDD Workflow Protocols
A resilient governance framework outlines clear operational boundaries between automated execution and human decision-making. When evaluating digital KYC vendors UAE compliance directors must ensure that automated alerts seamlessly transition into structured manual review channels.
| Trigger Event | System Execution | Analyst Action & Escalation | Governance Control Point |
|---|---|---|---|
| Biometric mismatch or low liveness confidence score | Flags profile; halts automated onboarding progression. | Conducts manual review of liveness payloads or requests secondary ID validation. | Analyst documents reason for override; requires Senior Compliance Officer co-signature for approval. |
| Fuzzy-matching sanctions or PEP alert generation | Generates pending alert status; holds customer funds or account access. | Performs true-match analysis against official watchlists and global intelligence databases. | Confirmed matches trigger immediate account block and goAML STR/SAR drafting workflow within statutory deadlines. |
| Unclear corporate structure or indirect foreign ownership | Parses visual corporate tree; flags missing ultimate beneficial owner (UBO) threshold. | Requests official certificate of incumbency, commercial register extracts, or foreign notarized organograms. | Manual UBO unwrapping log signed off by MLRO prior to final account activation. |
Regulatory Record-Keeping and Technical Archiving Standards
Ensuring CBUAE compliant digital identity onboarding extends to post-onboarding data lifecycle management. Compliance and IT departments must establish long-term archiving protocols for digital CDD files that satisfy both AML record-keeping mandates and UAE data protection standards.
All biometric liveness templates, verified document images, extraction metadata, liveness audit logs, and digital interaction records must be archived in encrypted, UAE-based data repositories for a minimum of five years from the date of account closure or transaction completion. Storage architectures must maintain high data integrity, ensuring that archived digital evidence remains unalterable, searchable, and instantly retrievable upon request by competent UAE regulatory authorities or law enforcement agencies.
Frequently Asked Questions
Can UAE financial institutions completely eliminate face-to-face onboarding using eKYC platforms?
Yes, CBUAE regulations permit full digital non-face-to-face onboarding, provided financial institutions utilize secure digital identity verification mechanisms like UAE PASS, robust biometric liveness detection, and verified real-time data sources while maintaining dynamic risk-scoring capabilities.
What are the primary Ministry of Economy rules for DNFBPs using digital onboarding software?
DNFBPs using digital onboarding software must ensure accurate identity verification, clear Ultimate Beneficial Ownership (UBO) identification down to 25% ownership, real-time sanctions screening against UAE local and UN lists prior to transaction execution, and maintenance of audit trails for five years.
Is a software vendor responsible if an eKYC platform fails to detect a sanctioned individual?
No. Under UAE federal AML laws, the regulated reporting entity (the bank, CSP, or DNFBP) retains legal responsibility and liability for regulatory compliance. Vendor technology is a tool, but compliance governance remains with the licensed entity.
How does digital KYC platform integration support goAML reporting in the UAE?
Compliant digital KYC software automatically captures customer identification, UBO data, source of funds documentation, and transaction histories, allowing compliance teams to efficiently compile structured data required for filing Suspicious Activity Reports (SARs) or Suspicious Transaction Reports (STRs) in the goAML system.
